Blog
Reflections on engineering, risk management and the current cybersecurity landscape.
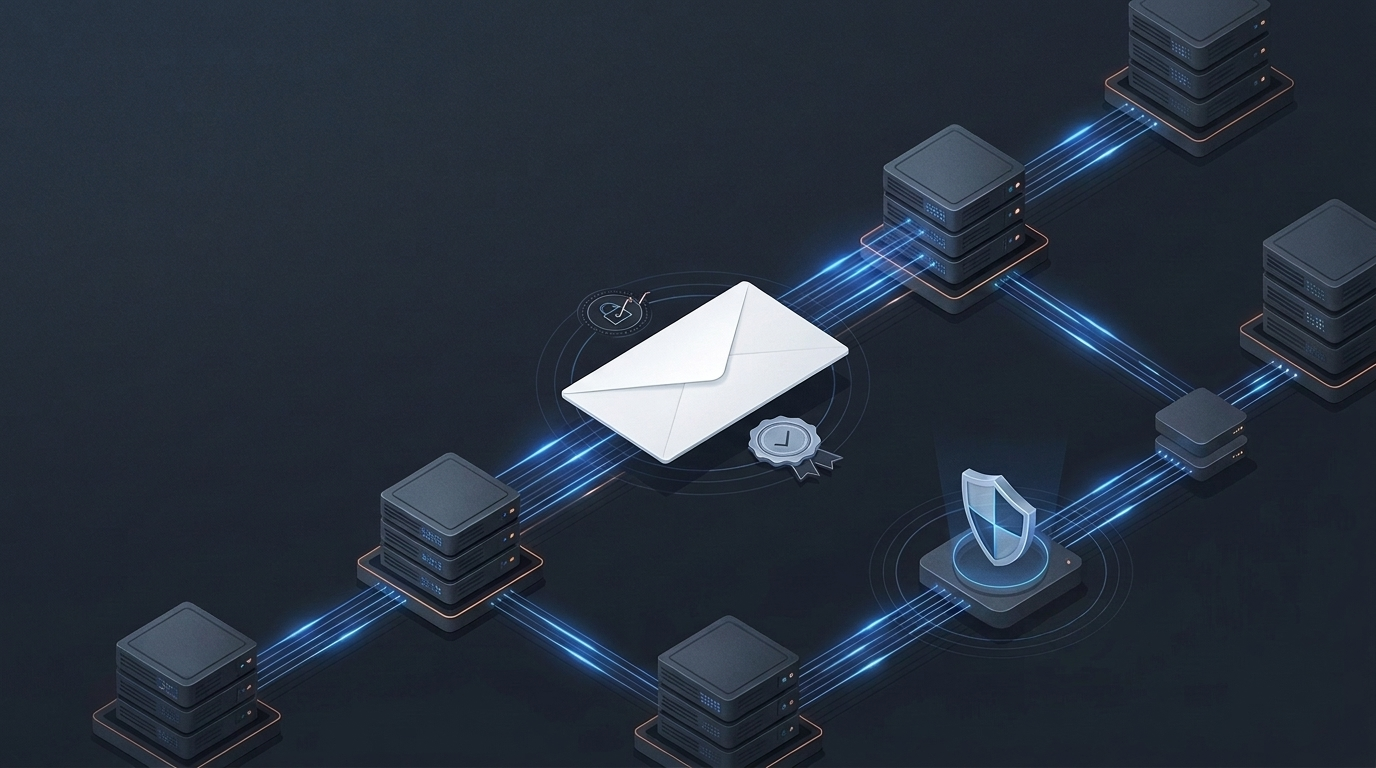
Email feels direct, but journeys through clients, servers, DNS, relays, and filters. Discover the protocols that protect it and where their limits lie.
Selling email databases is illegal, but reporting it is difficult. Discover free, legal strategies to neutralize spammers and protect your inbox privacy.

Content production has become effortless with AI. The bottleneck is no longer creating, but filtering. Human judgment has become the defining source of value.
A reflection on declining platform services, record corporate profits, and why cost cuts inevitably impact users and operational teams the most.
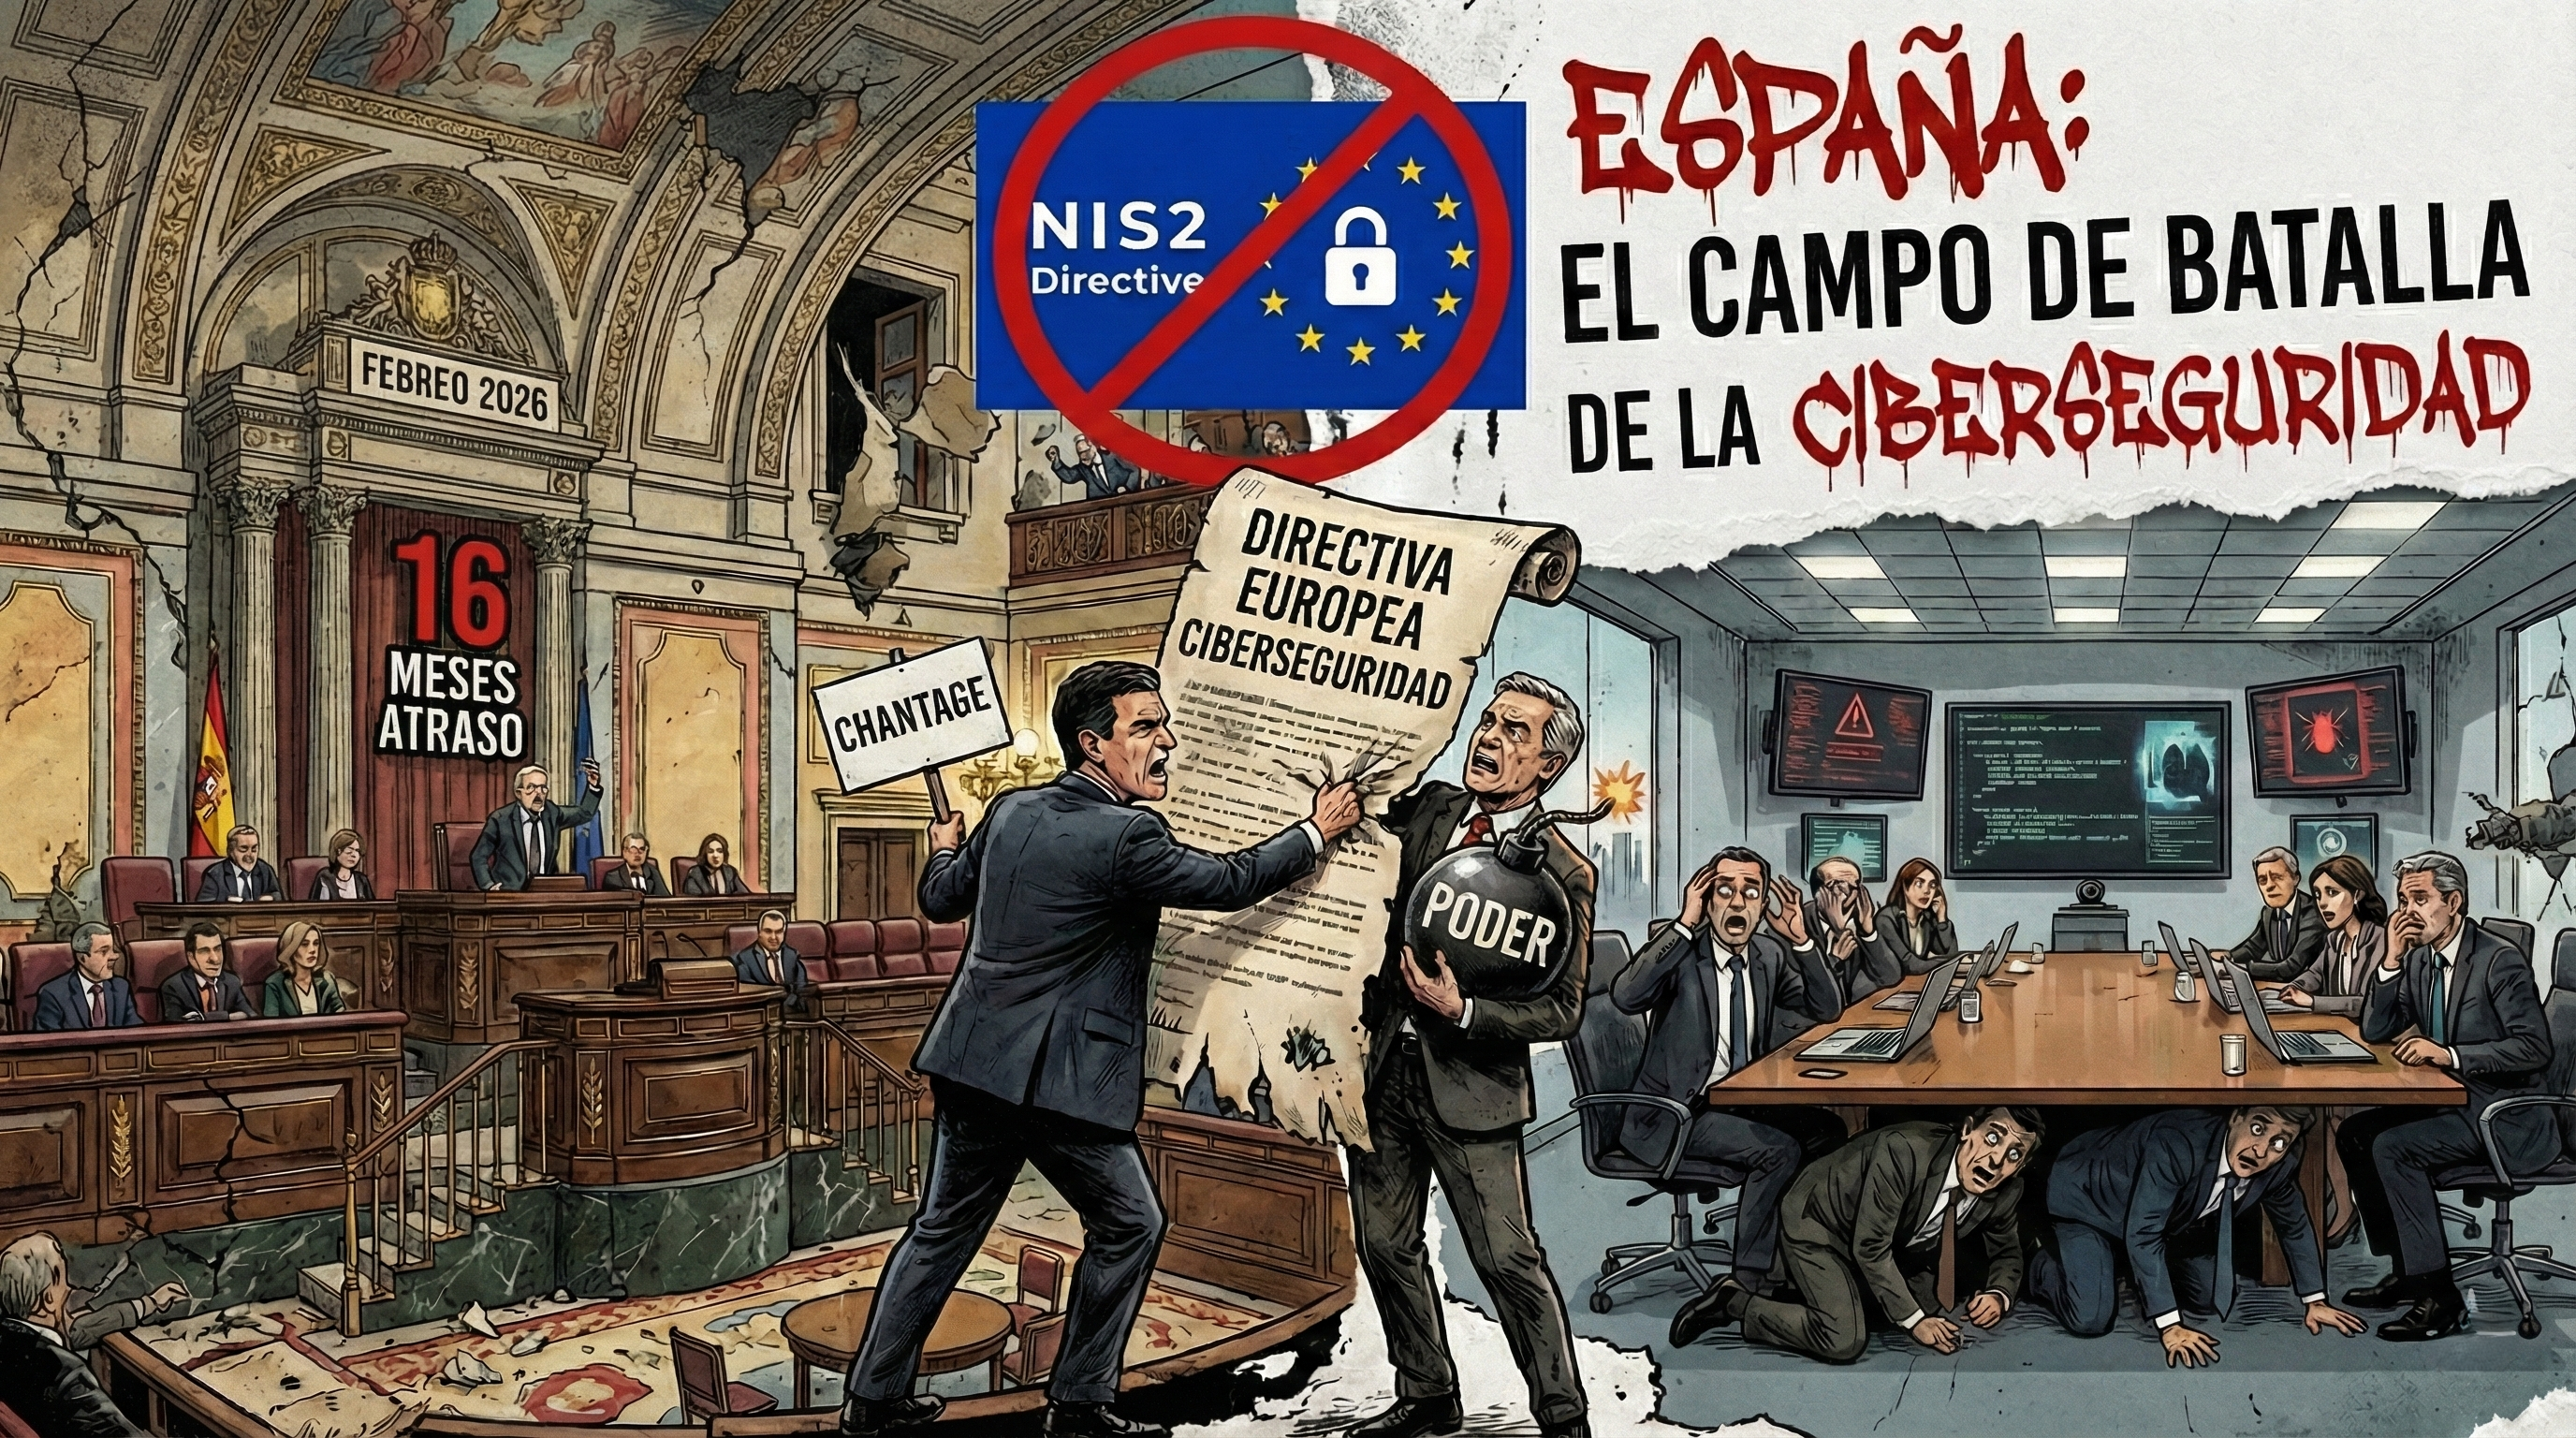
Spain faces significant delays transposing the European NIS2 Directive. Key insights on regulatory friction, funding at risk, and new corporate obligations.

Cloud infrastructure is not secure by default. Understand shared responsibility models and the critical misconfigurations that leave cloud workloads exposed.

Transform technical cybersecurity reports into strategic business decisions: the formula to translate technical vulnerabilities into financial impact for CEOs.
Incident response is not purely technical. Discover the psychological toll, anxiety, and burnout affecting response teams after a breach and how to manage it.
Behavioral biometrics analyzes typing rhythm, cursor movement, and interaction patterns for continuous, frictionless authentication. Discover its 2025 potential.
Third-party risk is the leading corporate intrusion vector. Discover how to assess vendor vulnerabilities and align with regulations like NIS2 and DORA.

How do you justify security budgets to the board? Learn how to calculate Return on Security Investment (ROSI) and communicate the financial value of defense.

Explore Gartner's CTEM framework: a 5-stage proactive approach to identify, validate, and prioritize vulnerabilities across your organization's attack surface.

Prevent email spoofing and Business Email Compromise (BEC) using SPF, DKIM, and DMARC: practical implementation steps to protect your brand reputation.

Review of the largest corporate data breaches of 2023: attack vectors, millions of exposed records, lessons learned, and defensive takeaways for organizations.
How password reset flows leak phone numbers and expose users to SIM swapping attacks. Technical breakdown and actionable mitigation steps for identity safety.
Highlights from Google's Cybersecurity Action Team report: emerging threats in cloud environments, typosquatting campaigns, and attack vectors in SaaS tools.
Analysis of TunnelCrack vulnerabilities in VPN clients: how attackers leak network traffic outside encrypted tunnels and how to properly secure remote workers.

Ransomware evolution, RaaS ecosystems, and double extortion threats: how to build a layered defense and incident recovery roadmap against cyber extortion.
Busting password strength myths: discover what genuinely makes credentials secure, how brute-force attacks work, and how to safeguard corporate access.
What is Data Security Posture Management (DSPM)? Discover how to locate sensitive cloud data, enforce governance, and prevent unauthorized exposure risks.

Discover how AI enhances social engineering through deepfakes and voice cloning, and learn the defensive strategies organizations need to prevent manipulation.
Learn how to protect your digital accounts from unauthorized access: best practices for strong passwords, two-factor authentication (2FA), and risk reduction.

Summary of the major personal data leaks and corporate breaches of 2022: human error, cyber attack patterns, and organizational contingency recommendations.